Updated: 20 October 2026
October marks Cybersecurity Awareness Month, and while many organizations focus on firewalls, phishing prevention, and endpoint protection, one critical area is often overlooked - the secure retirement of IT equipment. SK Tes urges businesses to think about what happens to their devices when technology is refreshed or employees leave the business and treat end-of-life hardware as a serious cybersecurity and compliance risk.
The Hidden Cybersecurity Threat in IT Equipment Disposal
When IT equipment reaches the end of its lifecycle and it is ready for disposal, it’s easy to assume that a factory reset or physical drive removal is enough to eliminate cyber security risk. But routers, switches, and hard drives can retain sensitive data long after they’ve powered down. Company credentials, network configurations, proprietary data, and even personal health or financial data have been found on dispositioned IT equipment, sometimes resold or dumped without proper and complete sanitization.
The role of cybersecurity and information management systems in the ITAD and e-waste industry cannot be overstated. As cyber threats continue to evolve and become more sophisticated we face increasing pressure to protect sensitive data throughout the entire lifecycle of electronic equipment.
Recent breaches highlight the risks:
- Refurbished routers sold online were found to contain corporate data, including credentials and network maps (Resource Reycling)
- A global data leak involving FortiGate firewall devices exposed configuration files and internal network details (Help Net Security)
- In the Netherlands, a man purchased hard drives filled with medical data at a second-hand market, revealing thousands of patient health records (ITpro)
- In the US, a stolen hard drive exposed personal health records for 76,000 patients, violating HIPAA regulations and more examples (HIPPA)
These incidents are not isolated cases. They highlight how weaknesses in end-of-life technology management can expose organizations to data breaches, regulatory scrutiny, and reputational damage.
Why Factory Resets of IT Equipment Aren’t Sufficient
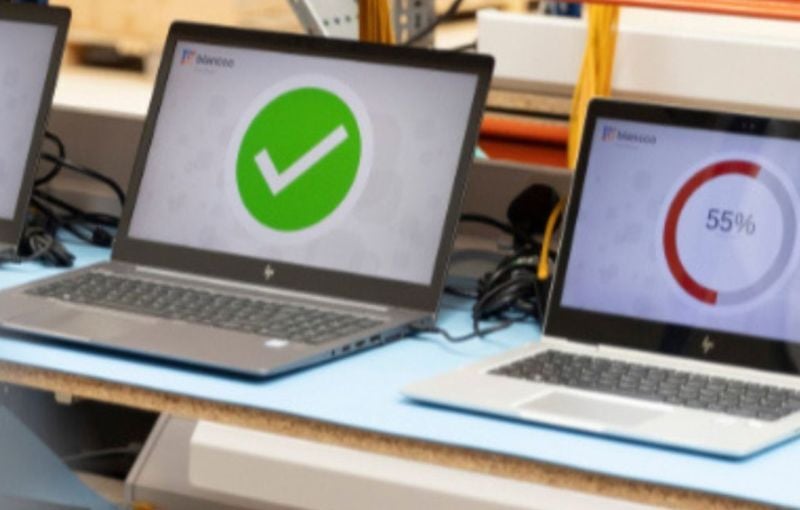
Some organizations rely on factory resets to ‘erase’ data. Unfortunately, this method often leaves recoverable traces of data. To completely protect sensitive information, data must be erased using recognized standards like NIST SP 800-88 and IEEE 2882-2022.
- NIST 800-88 outlines three levels of data sanitization: Clear, Purge, and Destroy. Clear uses logical techniques like overwriting, Purge involves cryptographic erasure or degaussing, and Destroy means physical destruction. The standard helps organizations choose the right methods based on data sensitivity, equipment type, and reuse goals.
- IEEE 2883:2022, a newer standard, addresses modern storage technologies like SSDs and NVMe drives. It also defines Clear, Purge and Destruct methods, but with updated guidance for newer devices. Notably, IEEE discourages shredding as a final solution, promoting environmentally sustainable practices and reuse where possible.
Both standards emphasize that verification is essential. Data erasure alone is not enough without documented proof that information has been permanently and irreversibly removed.
Global Data Regulatory Risks Are Real
Improper disposition of IT assets can lead to serious violations of global data protection laws.
An Overview of Key Data Protection Regulations:
- GDPR (General Data Protection Regulation): Applies to organizations handling EU citizen’s data. Mandates secure data processing and disposal. Breaches can result in fines up to €20 million or 4% of global turnover.
- UKDPR (UK Data Protection Regulation): The UK’s post-Brexit version of GDPR, it governs how personal data is processed and disposed of within the UK. Organizations must ensure that data on retired devices is securely erased to avoid breaches and penalties from the Information Commissioner’s Office (ICO).
- HIPAA (Health Insurance Portability and Accountability Act): US law protecting patient health information. Mishandling PHI, even on discarded devices, can lead to civil and criminal penalties.
- PCI DSS (Payment Card Industry Data Security Standard): Governs how businesses handle cardholder data. Retired devices with stored payment information must be securely wiped or destroyed.
- NIS2 (Network and Information Security Directive): EU directive requiring critical infrastructure operators to manage cybersecurity risks, including data disposal.
- DORA (Digital Operational Resilience Act): EU regulation for financial entities, mandating secure IT asset management and data protection throughout the lifecycle.
Breaching these regulations can result in fines, damage to your business reputation, and harm to customer trust.
Beyond avoiding fines, organizations should view secure IT retirement as an important component of broader information security and risk management programs. Demonstrating effective controls over retired devices through ITAD partner with recognized security certifications, documented procedures, and proven chain-of-custody processes can help build confidence with customers, investors, regulators, and other stakeholders.
Conclusion - A Better Way to Retire IT Equipment With SK Tes
As cyber threats continue to evolve, demonstrating responsible management of retired IT equipment is becoming increasingly important. Working with a trusted ITAD provider helps organizations reduce risk, strengthen governance, and build confidence among customers, partners, and regulators that sensitive information is being handled securely.
Organizations should also evaluate the security practices of third-party providers handling retired technology. Secure chain-of-custody controls, verified data sanitization, and adherence to standards such as ISO/IEC 27001 help ensure data remains protected throughout the retirement process while supporting compliance and audit requirements.
SK Tes offers certified data destruction, secure logistics, and complete audit trails as part of its global IT asset disposition (ITAD) service, helping organizations protect sensitive information while meeting security and regulatory requirements.
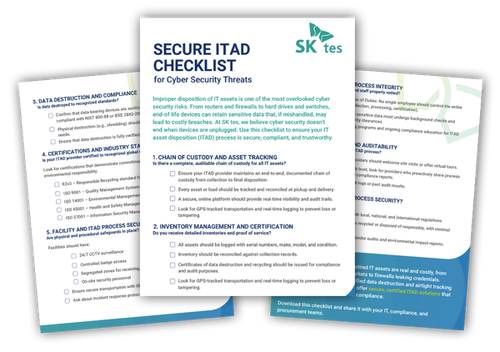
To help your business or organization retire IT assets, we are offering a free 8-point Checklist for Secure IT Asset Disposition.
Secure ITAD Checklist for Cyber Security - SK Tes
Prevent cyber security threats, data breaches and regulatory issues.
Access the secure ITAD checklist to keep your IT retirement process secure and compliant.
This blog is written by:
Tom Hoof, Group IT Director
Tom Hoof is the Group IT Director at SK Tes, a leading global technology and IT lifecycle services firm. With over two decades of experience in enterprise IT strategy, infrastructure, and digital transformation, Tom has been instrumental in driving innovation and operational excellence across the organization. Known for his pragmatic leadership and deep technical insight, he oversees global IT initiatives that align with business goals and future-proof the company’s digital capabilities. Passionate about cybersecurity, cloud architecture, and emerging tech, Tom is a frequent contributor to industry panels and thought leadership forums.
Get in touch with us, contact us.
Related posts
AI Is Accelerating Data Center Refresh Cycles. ITAD Must Keep Pace
Read more
Inside Data Center Decommissioning at Scale
Read more